Single sign-on over SAML or OAuth, SCIM provisioning and optional two-factor authentication, so IT keeps control of who gets in.




ChangeEngine supports single sign-on over SAML or OAuth and SCIM provisioning, so IT controls who can edit and publish.
See every integration →Identity attributes for sign-in and provisioning. Audience data comes from your HRIS.
IT controls access and provisioning. Editors only see what their role allows, and every change is logged.
Editors only see what their role allows, and every change is logged.
When something changes in your system of record, the right people hear about it on the right channel. Nobody on the People team presses send.
Provision a new ChangeEngine editor through your identity provider.
Editor access follows the role IT assigns.
Deprovisioning removes access without a separate ticket.
Employees reach the hub with Google or Microsoft sign-in, or from a link.
Word-level audit logs show who changed what.
Access reviews run in the identity tools IT already uses.
SAML or OAuth SSO for everyone who edits in ChangeEngine.
Create and remove editor access from your identity provider.
Optional 2FA for editors.
Editors see and change only what their role allows.
Word-level audit logs for every change.
SOC 2 and ISO 27001 certified, GDPR compliant.
Editors sign in to ChangeEngine through your identity provider over SAML or OAuth, with optional two-factor authentication.
Create and remove editor access from your identity provider, so access follows the people IT already manages.
Employees read messages where they already are and reach the hub from a link or with Google or Microsoft sign-in.
Your services team runs the setup with IT. When you need something that is not in the box, your forward deployed engineer builds it.
Meet the forward deployed engineer →IT shares the identity provider details. We send the checklist ahead of the call.
We configure SSO and, if you want it, SCIM provisioning together.
Editors sign in through your identity provider from day one.
Your People team moves fast. Your IT team keeps control of every connection.
SOC 2 and ISO 27001. GDPR compliant, with data residency in the US, EU or Canada.
Single sign-on over SAML or OAuth, with optional two-factor authentication for editors.
SCIM provisioning, and content shown by HRIS attributes like role, location and employment type.
Employee data is encrypted in transit and at rest, and editors only see what their role allows.
Word-level audit logs, role-based editors, and AI providers contractually barred from training on your data.
Run your hub on your own subdomain, like central.yourcompany.com, with a couple of DNS records.


Any provider that supports SAML or OAuth single sign-on.
No. Employees read messages where they already are and open the hub from a link. Editors sign in.
Yes. SCIM provisioning is available for editor accounts.
Yes. Optional 2FA is available for editors.
In the ChangeEngine Trust Center.
Yes. SOC 2 and ISO 27001 certified and GDPR compliant.
The ChangeEngine MCP connects the assistant your company already approved. Build audiences from this integration's data, draft a send or pull last week's read rates in plain words. A person on your team publishes every send.
Explore the ChangeEngine MCP →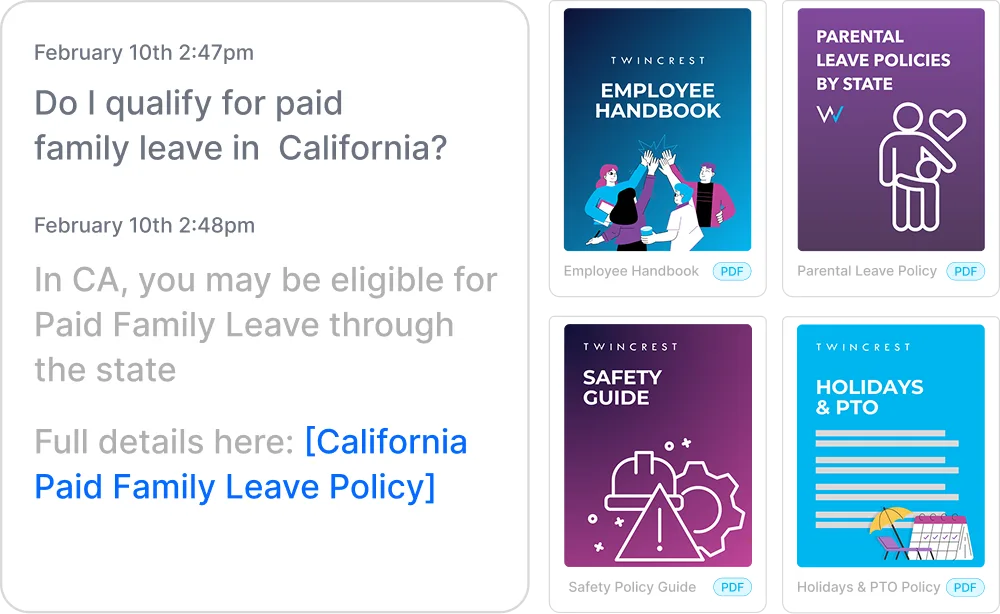
Instant, policy-grounded answers in the hub and Slack/Teams.
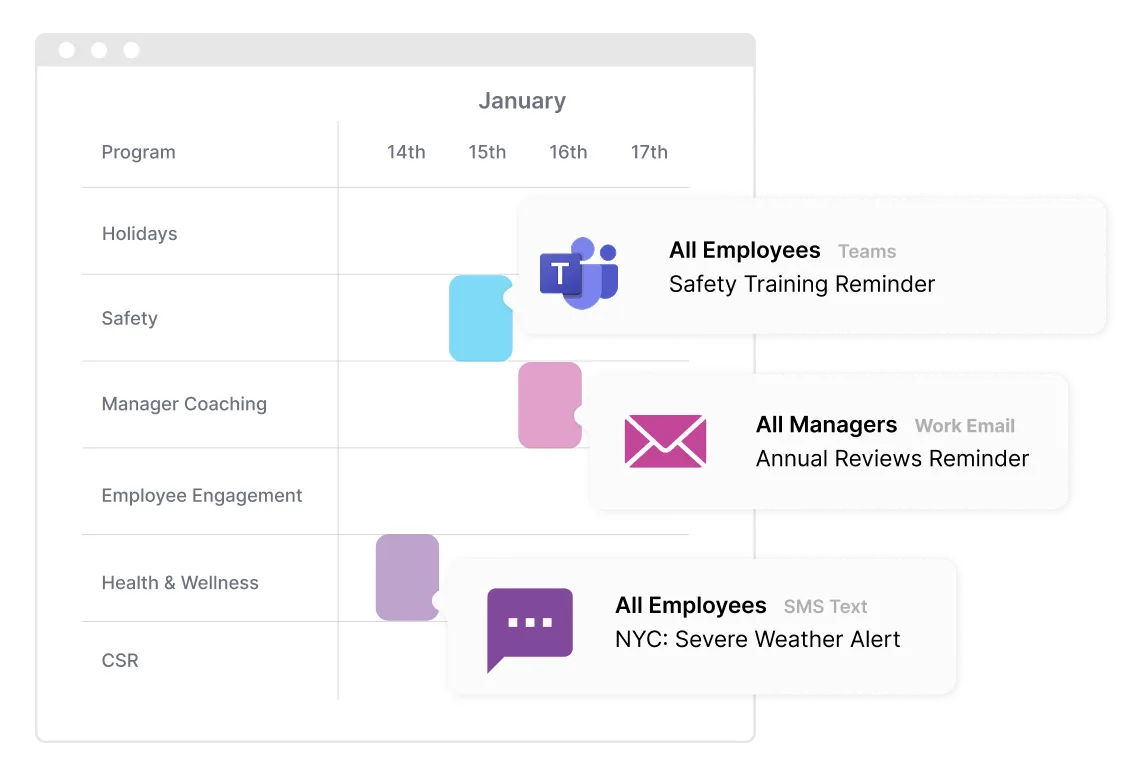
One message, every channel, timed to each person.
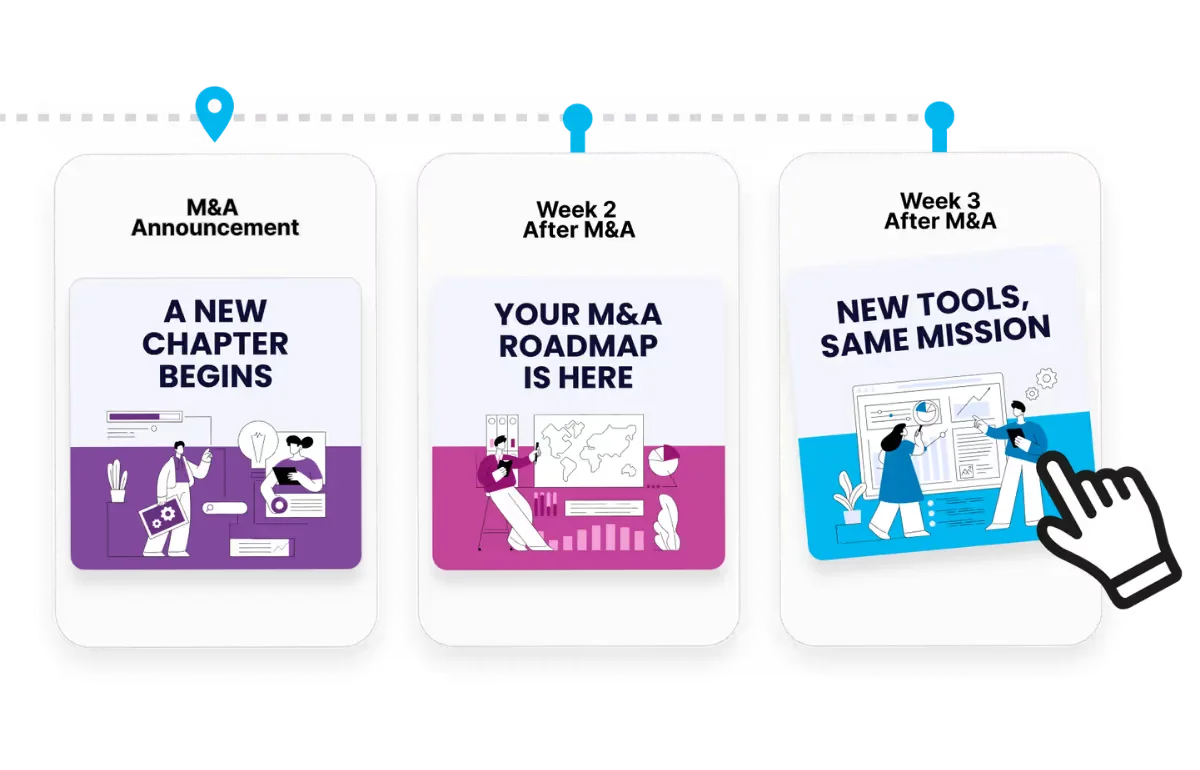
Onboarding to offboarding, triggered by your HRIS.
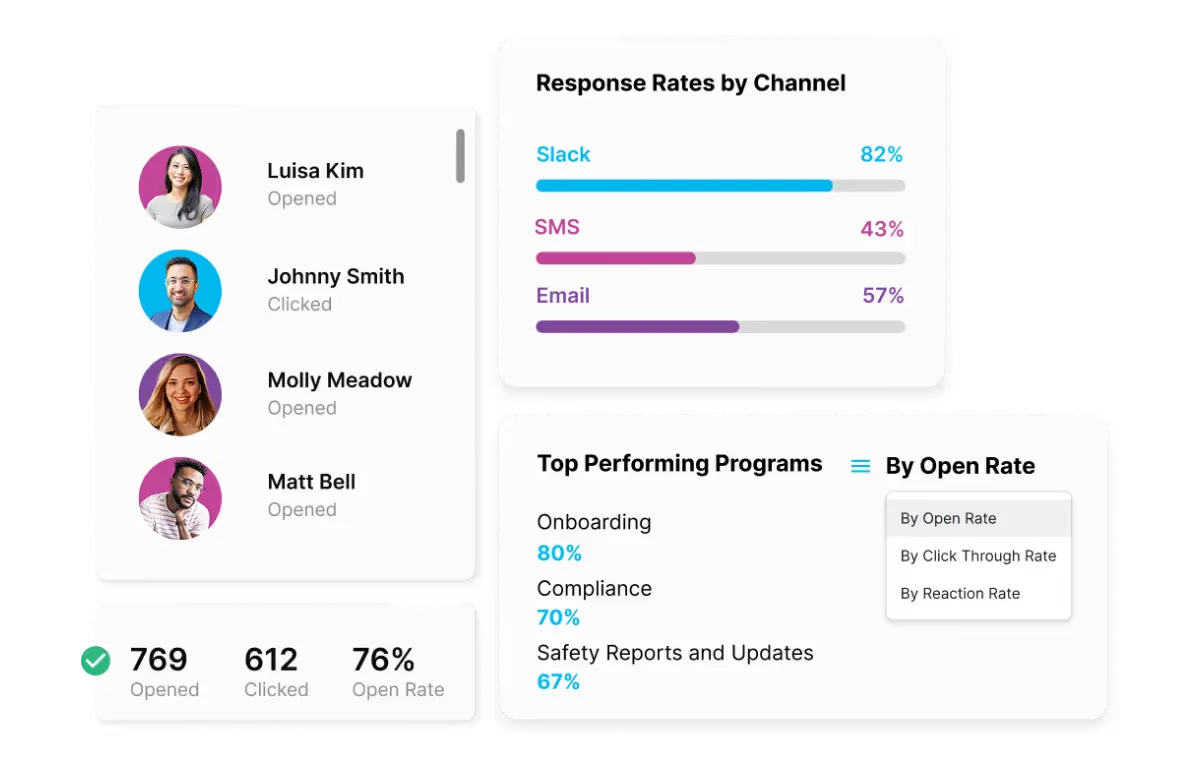
Proof for leadership, by team, channel and program.
Bring your HRIS and your channels. We will show you your first program, built in front of you.